What Have I Been Pwned does
Have I Been Pwned lets you check if your email address or a password has appeared in a known data breach. Paid plans add an API, domain monitoring, and stealer log data for organizations.
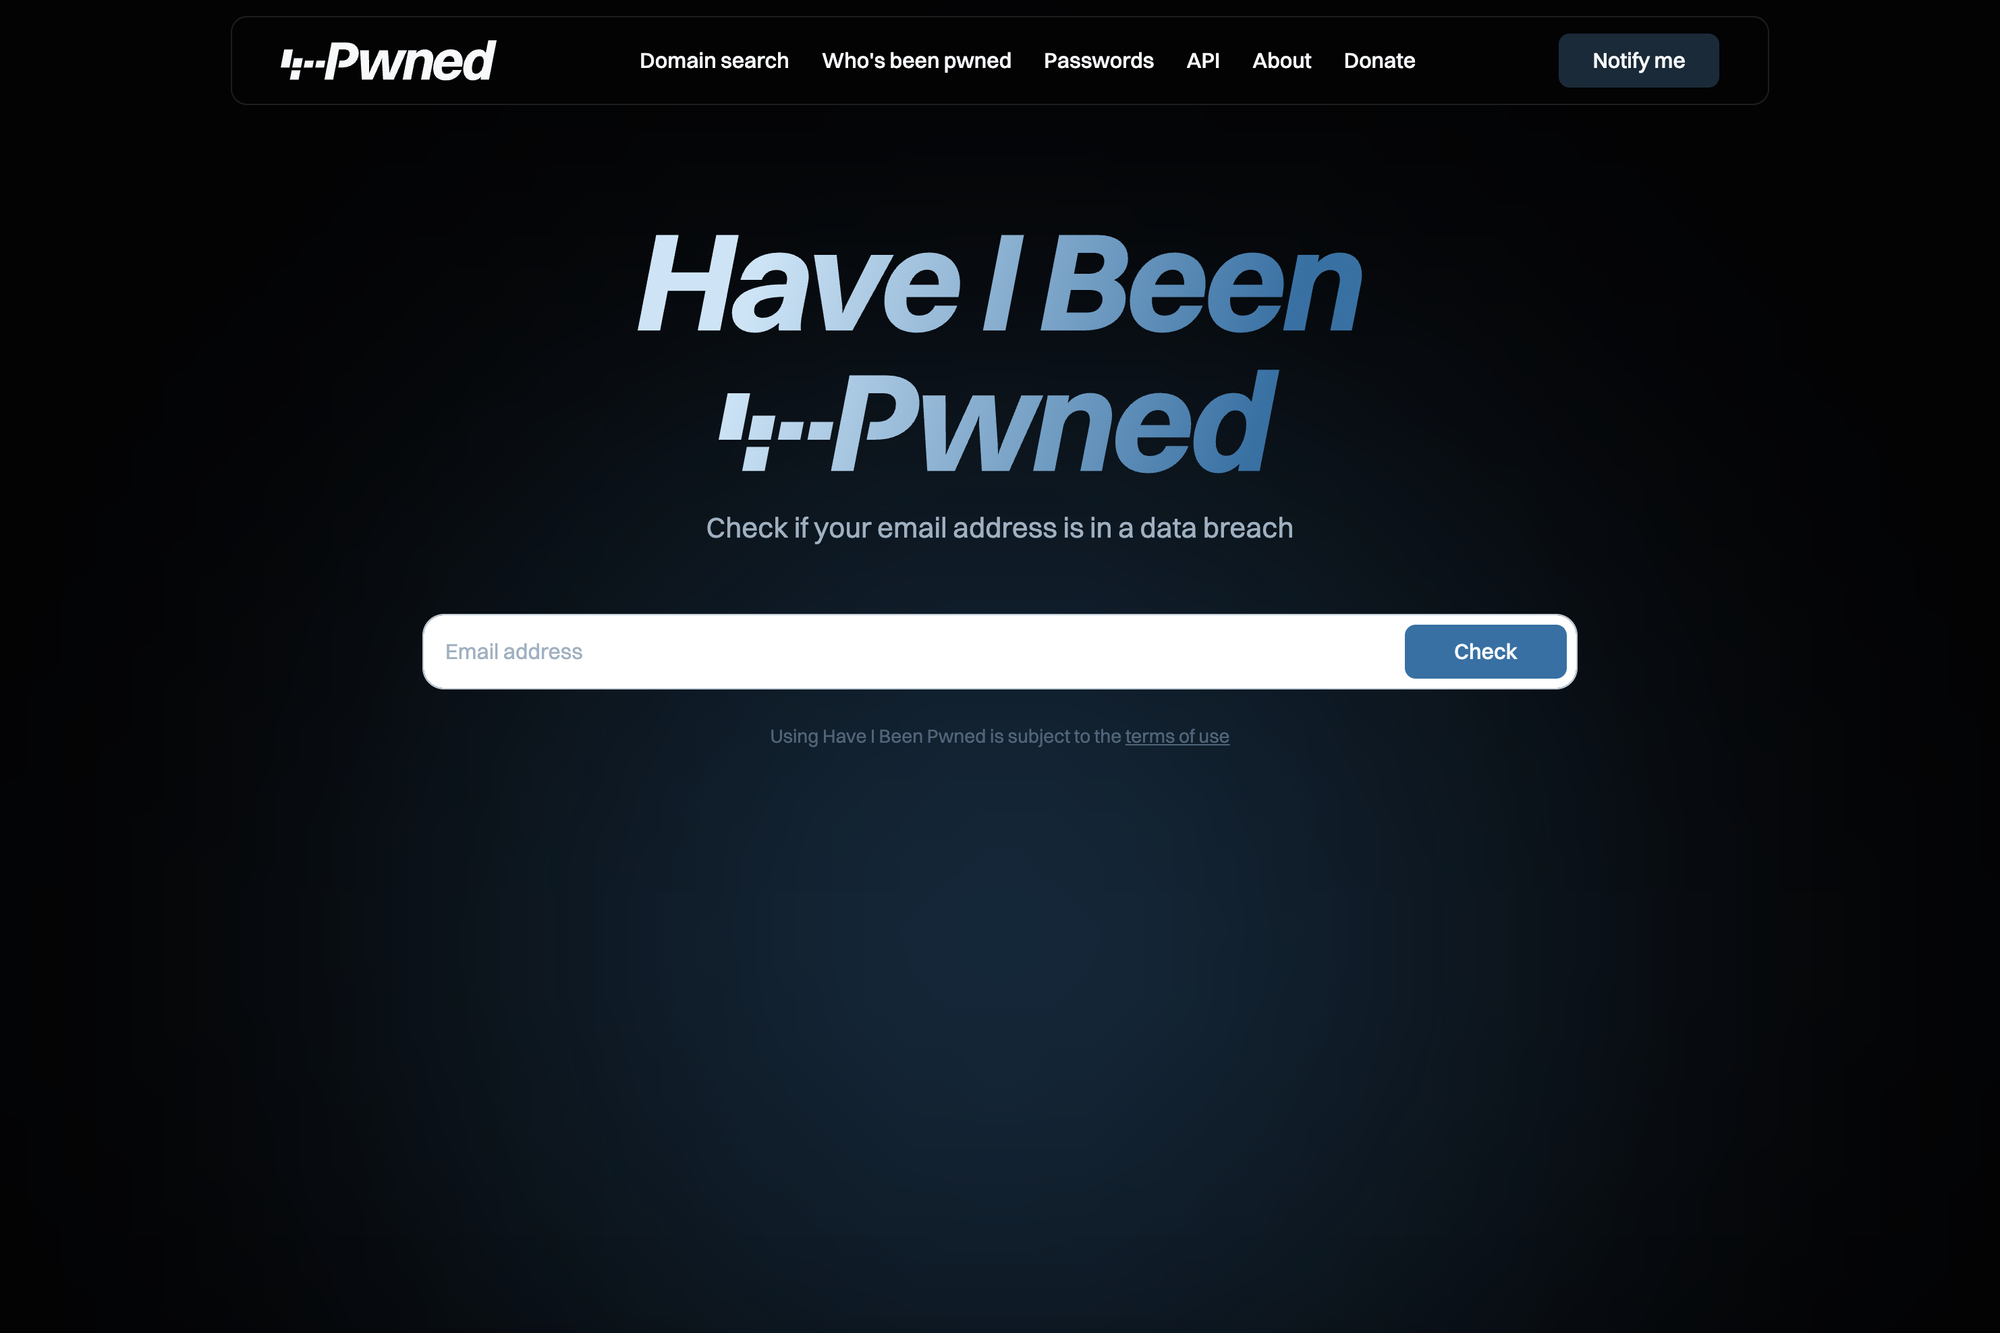
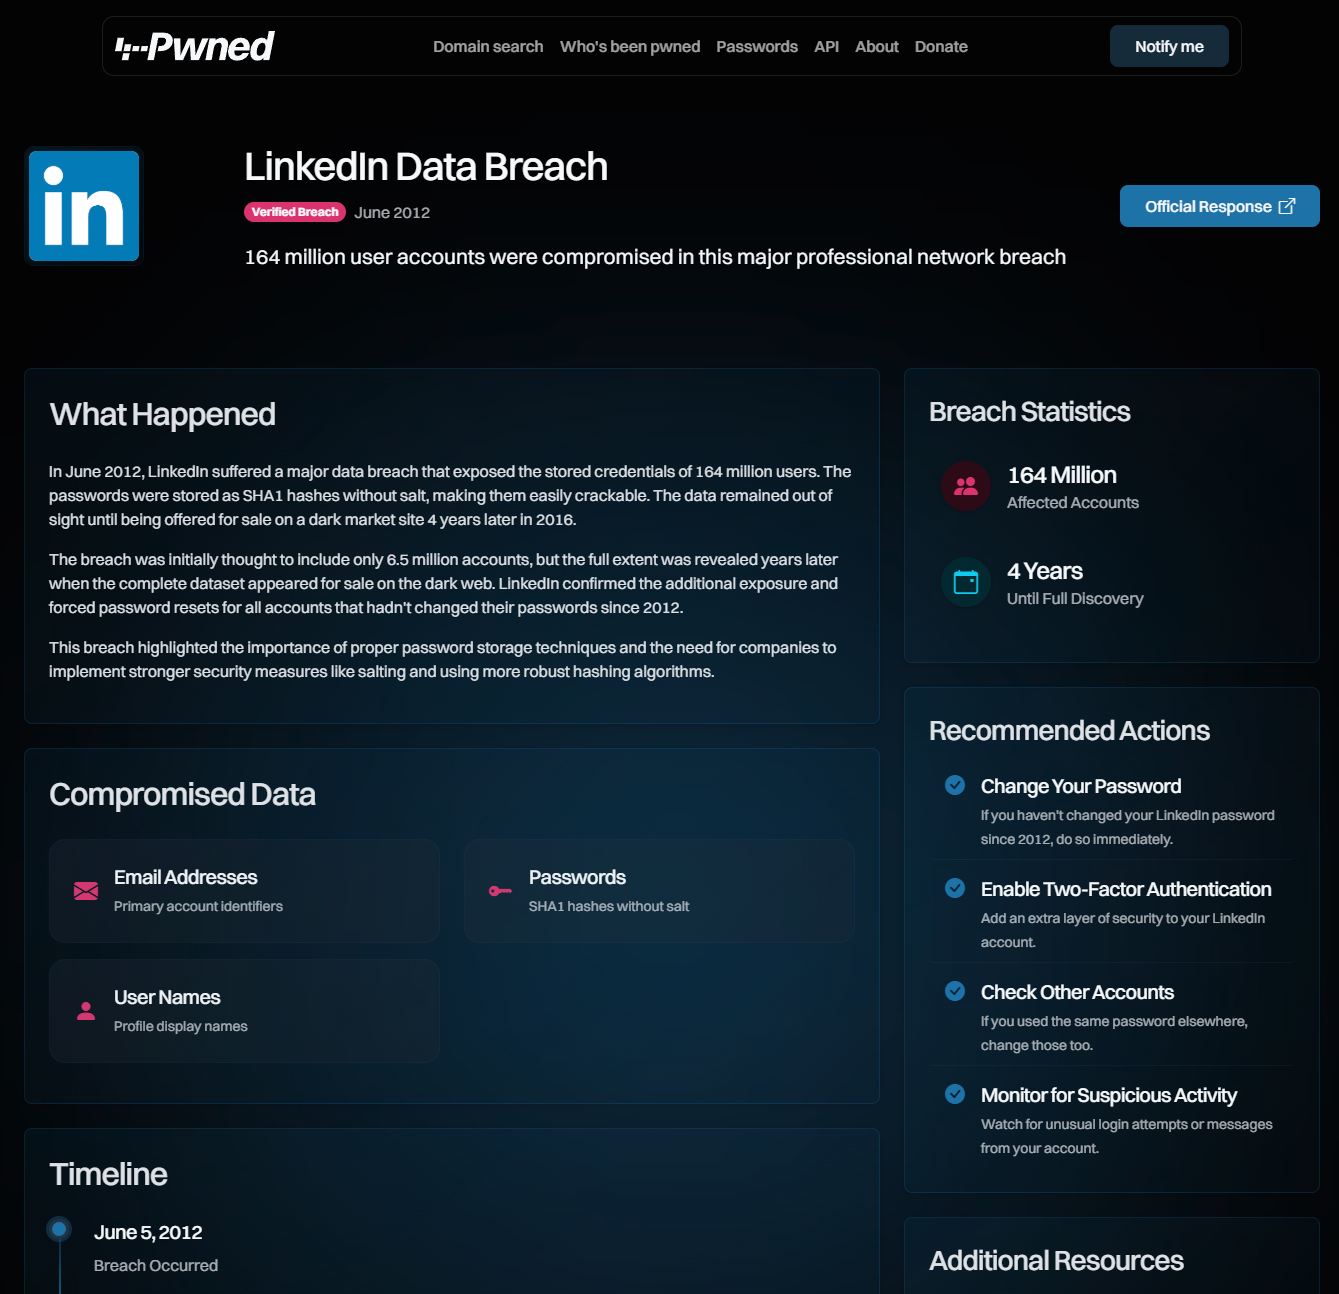
Have I Been Pwned, often shortened to HIBP, is a search and notification service for data breaches. You enter an email address on the website and see a timeline of the breaches and pastes that exposed it, along with the kinds of data that leaked. The service holds more than 17 billion breached addresses from over 1,000 breached websites.
The free features cover most personal needs. Browser email search, email notifications through Notify Me, and Pwned Passwords cost nothing. Notify Me sends you an email when your address appears in a new breach. Pwned Passwords checks whether a password has been seen in a breach, using SHA-1 hashes and k-anonymity so the full password is never sent, and it is free and open source. HIBP does not store passwords next to email addresses and does not send exposed passwords to anyone.
For organizations, a dashboard verifies control of a domain and then shows every breached address on it. Paid subscriptions add API access for email search and domain monitoring. Core plans start at $4.39 per month billed annually, Pro plans add k-anonymity email search, customer domain monitoring for MSPs, and stealer log data, and High RPM plans serve high-volume API use. A free tier also allows breach monitoring for domains with up to 10 breached addresses.
The REST API is documented on the site, and an MCP server lets AI agents query breach data, domains, and Pwned Passwords with OAuth sign-in. Public breach metadata and Pwned Passwords range searches work without signing in.
Troy Hunt, a security researcher and speaker, created HIBP in 2013 after the Adobe breach. He runs it with Charlotte Hunt, who manages operations, and Stefán Jökull Sigurðsson, who maintains the code and cloud infrastructure. The site says the service is independently owned and is used by law enforcement agencies for breach victim notification.
Best for
Individuals who want to know if their accounts were exposed, and security teams, developers, and MSPs who monitor domains or check passwords at scale.
Not for
People looking for a password manager, antivirus, or identity theft insurance, as HIBP only reports known breach exposure.
Questions and answers
Is Have I Been Pwned free?
Yes for individuals. Browser email search, breach notifications, and Pwned Passwords are free. API access and larger domain monitoring need a paid plan.
Does HIBP store my password?
No password is loaded with breached email addresses. Pwned Passwords stores SHA-1 hashes with no link to personal data such as email addresses.
Can I see all breached addresses on my company domain?
Yes, after you verify that you control the domain. The free tier covers domains with up to 10 breached addresses, and paid plans cover larger domains.
How much does the API cost?
Core plans start at $4.39 per month billed annually. Pro and High RPM plans add higher rate limits, k-anonymity search, and stealer log data.
Can AI agents use HIBP?
Yes. HIBP runs an MCP server at haveibeenpwned.com/mcp. Public breach data works without sign-in, and account and domain tools use OAuth.